Xtant.tech Logo

Intelligence with
Accountability.

You're shipping AI faster than your policies can keep up. We help you inventory every model, control how it behaves, and get ISO/IEC 42001 ready, so customers, investors and regulators can trust what you've built.

Book a free scoping call

Led by an ISO/IEC 42001 and ISO/IEC 27001 Lead Auditor.

Ask Clarity AI: Instant Compliance Advisory
ISO/IEC 42001GOVERNANCESECURITYCOMPLIANCEAUDITAI CORE
The Problem

Most companies build AI.
Few govern it.

Ask a typical AI team three questions: Which models are running in production right now? Who approved them? What happens when one gives a wrong answer to a customer?

Most can't answer all three. That gap shows up later, as a lost enterprise deal, a failed security questionnaire, or a regulator's letter.

AI without governance is just technical debt.

Every ungoverned model is a liability you'll pay for later, with interest. The cheapest time to fix it is before the audit, the incident or the investor's due diligence, not after.

Book a free 30-minute scoping call →
What We Do

One partner for AI governance,
from audit to enforcement

Consulting

ISO/IEC 42001 Consulting

We take you from gap analysis to certification-ready, with policies, risk assessments and controls built around how your team actually works.

Explore ISO Consulting
Security & ISMS

ISO/IEC 27001 Consulting

Information security that buyers and auditors recognise. We set up the controls, run the internal audit and prepare you for certification.

Explore ISO Consulting
Why Xtant.tech

Built by auditors and engineers,
not slide-makers

01

Governance-first

We start with the controls an auditor will ask for, so you don't rebuild later.

02

Engineering + compliance

Our team writes code as well as policy. Controls get built into your systems, not bolted on.

03

Direct Lead Auditor Access

Direct engagement with dual-certified Lead Auditors for ISO 27001 and ISO 42001 throughout every step of your project.

04

Future-ready

We build to ISO/IEC 42001 and track the EU AI Act and India's evolving AI rules, so you're not starting over when regulation lands.

Audit Readiness Lifecycle

From initial assessment to accredited certification

Phase 1: Gap Assessment & Scoping

We evaluate your current model pipelines, data flows, and documentation against ISO/IEC 42001 requirements to pinpoint exact compliance gaps.

Phase 2: Management System & Controls

We author your AI risk treatment plans, Statement of Applicability, and technical guardrails directly in your existing developer workflows.

Phase 3: Internal Audit & Certification

We conduct the mandatory independent internal audit, facilitate management reviews, and support your team throughout Stage 1 and Stage 2 audits.

Book a free scoping call
Team & Practice Leadership

The person you'll work with

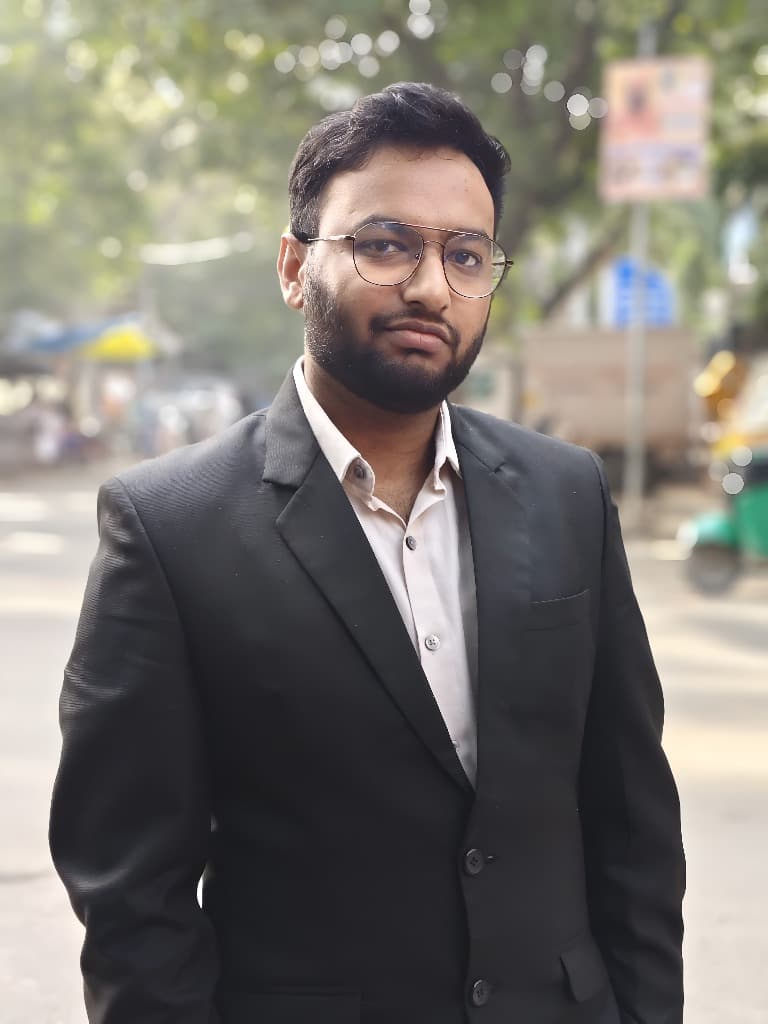
Ankit Kumar, ISO/IEC 27001 & ISO/IEC 42001 Lead Auditor
Certified Lead Auditor
ISO/IEC 27001 & ISO/IEC 42001 Lead AuditorFounder & CEO

Ankit Kumar

ISO/IEC 42001 and ISO/IEC 27001 Lead Auditor. Leads every consulting engagement and audit advisory.

Ankit bridges the divide between fast-moving machine learning engineering and formal international compliance. Having audited and implemented management systems across artificial intelligence (AIMS) and information security (ISMS), he guides AI startups and enterprises to audit-ready certification with practical, code-aligned governance.

ISO/IEC 42001 Lead Auditor (AIMS)
ISO/IEC 27001 Lead Auditor (ISMS)
Ready?

Let's make your AI assured.

Tell us what you're building and where it's headed. In 30 minutes we'll map your AI risks, show you where you stand against ISO/IEC 42001, and tell you honestly whether you need us.

Book a free scoping call

No commitment. No sales script. You'll leave with a short list of next steps either way.